Set up Single Sign-On (SSO)
Overview
This guide explains how to configure SAML 2.0 Single Sign-On (SSO) for Odin. SSO allows your users to authenticate through your organization’s identity provider (IdP), improving security and simplifying login management.
🔒 Important: Your IdP must be configured to sign SAML assertions, and you will need to upload your IdP’s x.509 certificate so we can validate them.
Who Can Configure SSO
SSO setup can be performed by users with one of the following roles:
- Admin – Has full administrative access.
- IT-Admin – A special role created for IT teams or consultants who need to configure SSO but do not require full access.
About IT-Admin
- Purpose: IT-Admins are meant solely for SSO configuration.
- Access: They can only access the SSO Setup page within Odin.
- Billing: IT-Admins do not count toward your organization’s seat count.
- Limitations: IT-Admins cannot:
- Access any other parts of the application
- View, create, or modify other user accounts
- Use the product beyond SSO configuration
💡 Tip: If your IT department or a third-party consultant is setting up SSO, assign them the IT-Admin role to avoid consuming paid seats.
Prerequisites
Before starting, ensure you have:
- An Admin or IT-Admin account in Odin
- Administrator access to your IdP (e.g., Okta, Azure AD, Google Workspace, Ping, OneLogin)
- One of the following:
- IdP Metadata XML file (recommended)
- Or, for manual entry:
- SSO URL (Single Sign-On URL / Login URL)
- Entity ID / Issuer
- x.509 Signing Certificate (Required)
- Your IdP must provide one valid certificate. This can be either:
- Included in the IdP metadata XML (recommended), or
- Uploaded separately in .pem, .crt, or .cer.
- If uploading separately, the file must include the standard PEM headers and footers
-----BEGIN CERTIFICATE-----
[certificate content]
-----END CERTIFICATE-----
Some IdPs (e.g., Keycloak, PingFederate) export certificates without these lines, in which case you’ll need to add them manually.
- The certificate must match the one your IdP uses to sign SAML assertions.
- If multiple signing certificates are available (for rollover), choose the one currently in use.
Configure SSO
Step 1: Enable SSO
- Log in to Odin as an Admin or IT-Admin.
- Navigate to Account Settings -> Organization Settings.
- Toggle Enable SSO for all members (this will require all users except Admins and IT-Admins to sign in with SSO).
- Review the confirmation modal carefully:
- Password-based login will be disabled for standard users.
- Admins and IT-Admins will always be able to log in using both password and SSO — you cannot lock yourself out.
- Make sure you have IdP credentials and a test user account ready.
- Click Enable SSO to proceed to configuration.
⚠️ Trouble accessing this page? If you don’t have access or see an error enabling SSO, contact [email protected].

Step 2: Review “Our Config”
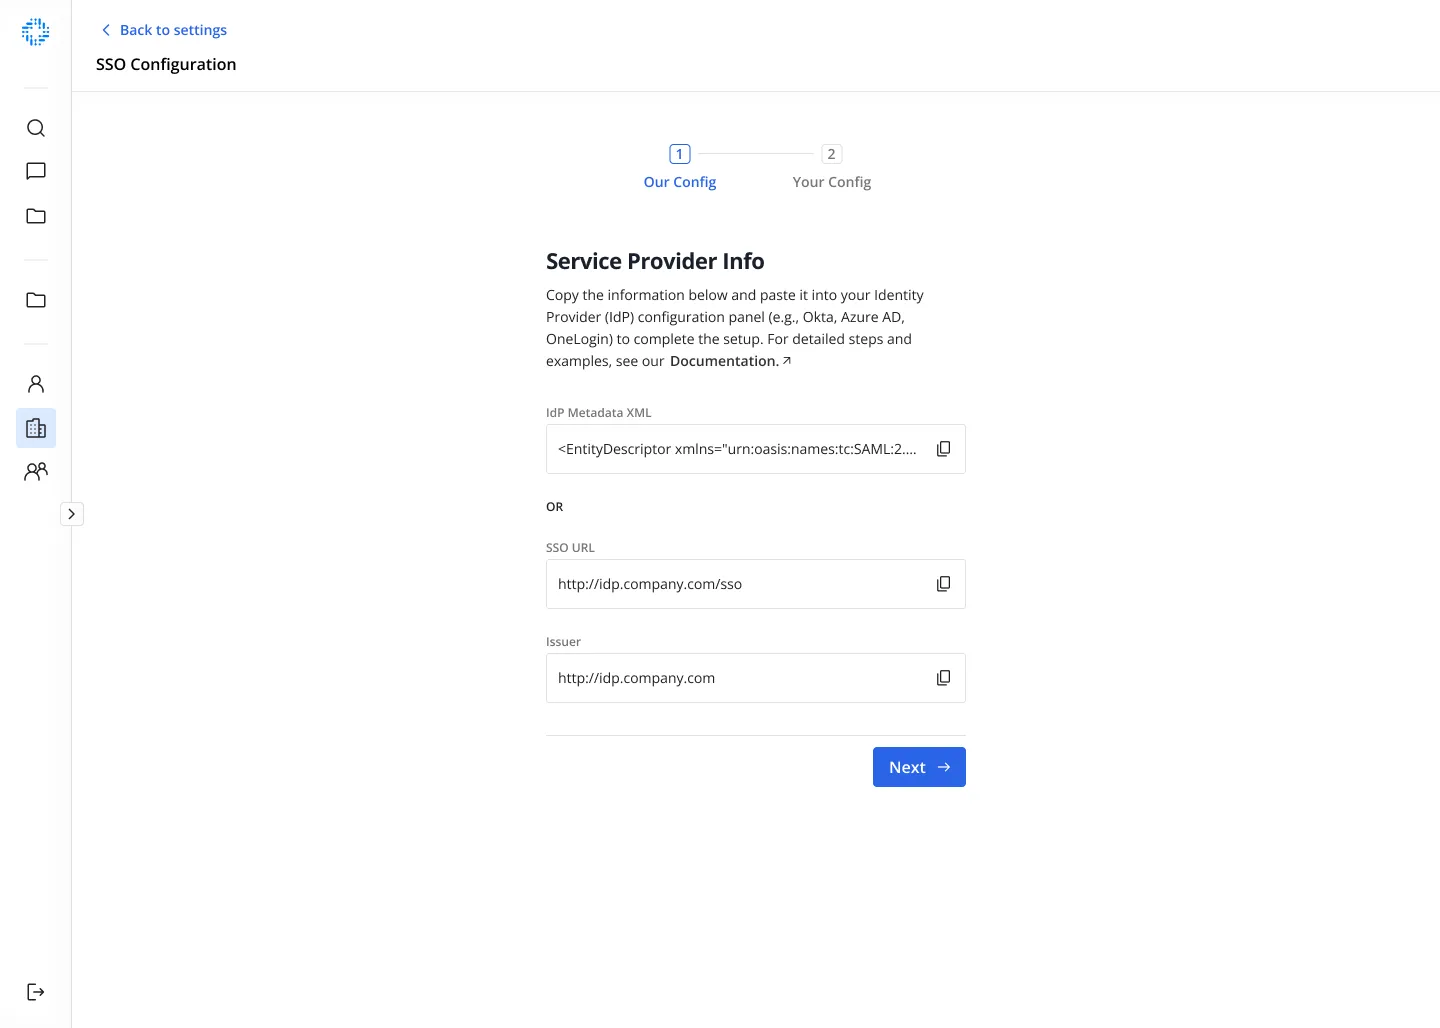
You’ll now see the Our Config section of the SSO Configuration wizard. This page shows the Service Provider (SP) information. You can configure your IdP using either of these approaches:
Option 1 (Recommended): Use the SP Metadata XML
- Copy the XML provided and paste it into your IdP’s SAML configuration.
- Most IdPs can import this XML to automatically configure ACS URL, Entity ID, and NameID format.
Option 2: Manually copy each field
- SSO URL (ACS URL) – paste this into your IdP’s Assertion Consumer Service URL field.
- Issuer (SP Entity ID) – paste this into your IdP’s Entity ID or Audience field.
💡 Tip: Keep this page open while setting up your IdP so you can easily copy values.
Once your IdP is configured, click Next to continue.
Step 3: Complete “Your Config”
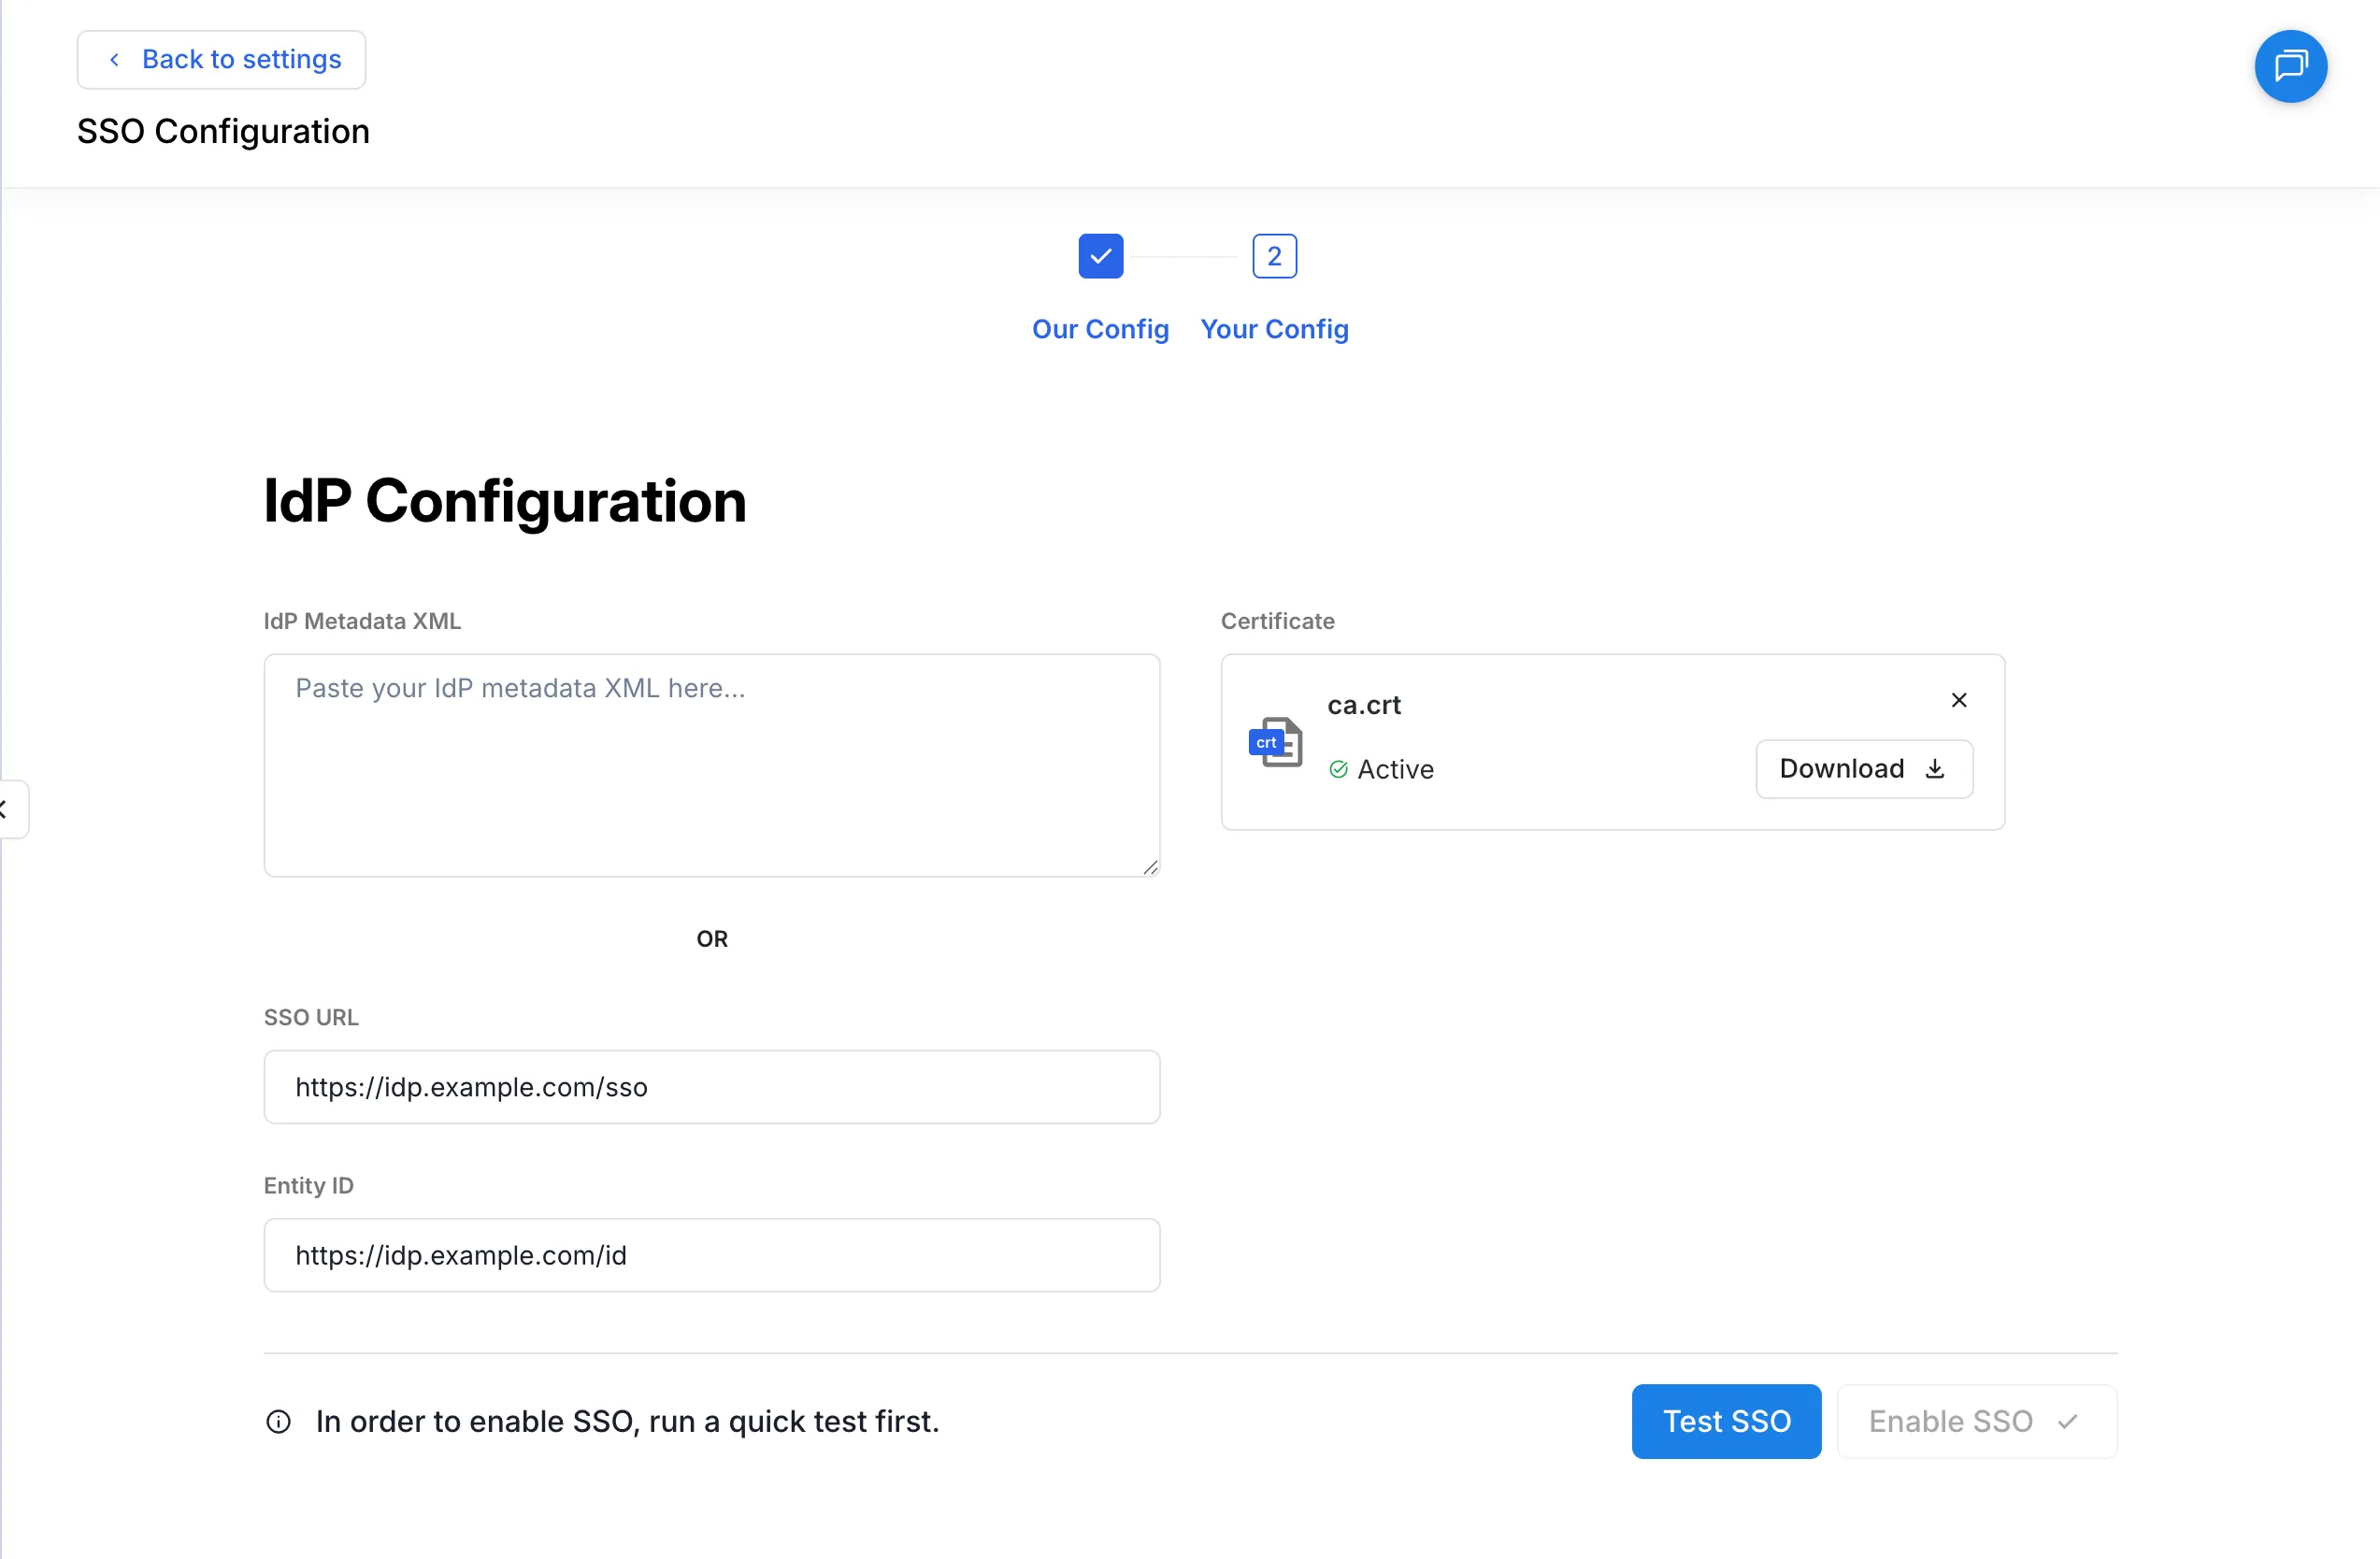
In the Your Config section, you’ll provide your IdP details back to Odin:
- Enter IdP Metadata or Manual Values
- Option 1 (Recommended): Paste your IdP Metadata XML into the field.
- Option 2: Enter your SSO URL and Issuer manually.
- Upload Signing Certificate
- The system requires one valid X.509 certificate. You can provide it in either of two ways:
- If your IdP metadata XML already includes the certificate, no additional upload is needed.
- If uploading separately (.pem, .crt, or .cer), make sure the file includes the PEM headers and footers:
-----BEGIN CERTIFICATE-----
[certificate content]
-----END CERTIFICATE-----
Without these wrappers, the upload will fail.
🔒 Important: You must explicitly upload the certificate you want to trust, even if it is included in the metadata XML. This ensures you intentionally select the correct signing key.
Step 4: Test and Enable SSO
- After you've filled in the details, you need to test the SSO config before it can be enabled.
- Hit the Test SSO button at the bottom of the page, this will redirect you to your IdP and initiate a mock sign-in attempt.
- If the sign-in attempt succeeds you can enable SSO by clicking the Enable SSO button.
- In case of failure or abandonment of the test, the Enable SSO button remains disabled and you will need to refresh the "Your Config" page to test again
✅ Reminder: Admins and IT-Admins can always log in with either password or SSO even after enforcement is turned on; this ensures you cannot accidentally lock yourself out.
Step 5: Certificate Maintenance (Recommended)
- Only one signing certificate can be active at a time.
- If your IdP rotates keys, update the certificate in Account Settings -> Organization -> Change SSO configuration page before the old one expires.
- Keep at least one Admin or IT-Admin credential with password login as a fallback in case of IdP issues.
User Provisioning and Supported SSO Claims
Supported Identity Features
Odin does not support Just-In-Time (JIT) provisioning or SCIM-based user synchronization. All users must be manually registered and invited through the web application before they can access the platform (see Inviting team members to your organization and User sign up and account management).
If Single Sign-On (SSO) is enabled for your organization, invited users may use it to sign up and sign in, as long as the email address used for SSO matches the one associated with their registered Odin account.
SSO Assertions and Claims
Odin does not process or rely on any additional claims or assertions beyond those required for authentication. Specifically:
- The SAML assertion urn:oasis:names:tc:SAML:2.0:assertion:NameID must contain the user’s email address.
- That email address must exactly match the email registered in Odin.
- No other SAML attributes or OIDC claims are consumed, although they are stored.
This ensures that user identity is verified solely based on existing account records in Odin.
Support
If you need assistance:
- Email: [email protected]
- Live Chat: Available in Odin